A booby-trapped Brotli stream can overflow memory in .NET apps, no login needed. Microsoft shipped emergency fixes on October 25 (CVE-2026-111497).
What happened:
A flaw in the decoder for Brotli, Google's compression format, lets a malicious compressed stream overflow the decoder's memory. That can leak data, crash the app, or potentially run code.
Am I at risk?
Yes, if your app decompresses Brotli data from untrusted sources. .NET Framework is not affected.
Severity:
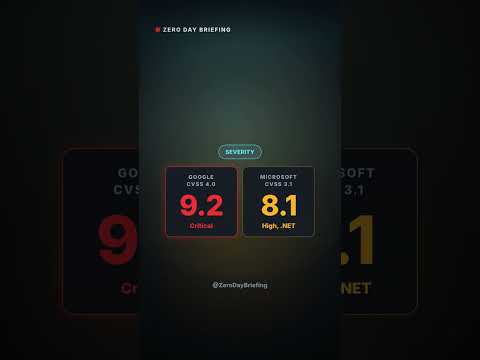
Google rates it 9.2 out of 10 (CVSS 4.0). Microsoft rates the .NET impact 8.1 (CVSS 3.1). No attacks in the wild have been reported yet.
Fixed versions:
.NET 8 to 8.0.33
.NET 9 to 9.0.22
.NET 10 to 10.0.14
Node.js and Python's brotli package have shipped fixes too.
What to do:
Install the update, restart your apps, and rebuild and redeploy self-contained apps. If you cannot patch yet, stop decompressing untrusted Brotli data.
Sources: Microsoft advisory (github.com/dotnet/announcements/issues/494), CVE record (cve.org/CVERecord?id=CVE-2026-111497)