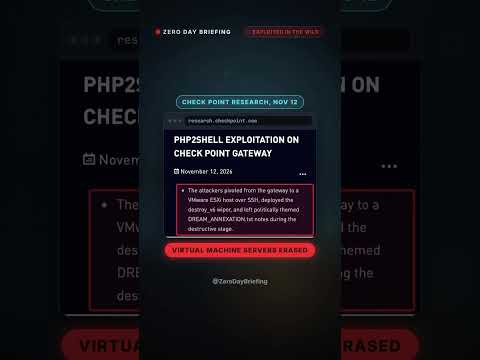
A Check Point firewall zero day was used to get root, then attackers wiped VMware ESXi servers behind it.
CVE-2026-123039 is a local privilege escalation in Gaia OS (CVSS 7.8, High).
What happened:
According to Check Point Research, as reported by BleepingComputer, attackers got in through the Mobile Access portal using the PHP2Shell bugs that PHP patched on October 21. They then used this bug to become root on the gateway and move to the virtual machine hosts.
The bug needs a foothold first. It is not a remote bug on its own.
The numbers:
Check Point says it saw the zero day exploited against a couple of dozen customers. That is the count for the zero day, not for wiped servers.
The wiping was seen in the first wave on October 30.
CISA added the CVE to its Known Exploited Vulnerabilities catalog on November 13, with a federal due date of November 16.
The fix:
Install the Jumbo Hotfix.
Fixed takes: R82.20 Take 14, R82.10 Take 52, R82 Take 132 and R81.20 Take 174.
R81 and R81.10 are end of support with no fix listed, so upgrade.
Then check exposed gateways for signs of a break in.
Advisory: Check Point sk1000362.
Sources: Check Point advisory sk1000362, Check Point Research, BleepingComputer, CISA KEV catalog.