A new Java flaw could let strangers take over servers, and it sits in Java itself.
Java4Shell (CVE-2026-114938) is in the Java runtime, in the code that decodes Base64 data.
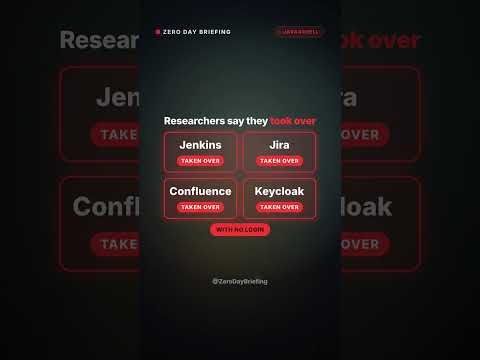
Researchers say they demonstrated takeovers of Jenkins, Jira, Confluence and Keycloak with no login. These were demos, not real attacks.
They say they found it with an AI in about an hour.
Who is affected: Java 17 and newer on servers with recent Intel and AMD chips.
No attacks had been reported as of Nov 17, 2026. Oracle shipped fixes that day, and other Java distributions are following.
What to do: update your Java runtime, including the copies bundled inside your apps and container images.
Sources: CVE.org CVE-2026-114938, OpenJDK advisory Nov 17 2026, BleepingComputer, Qualys.