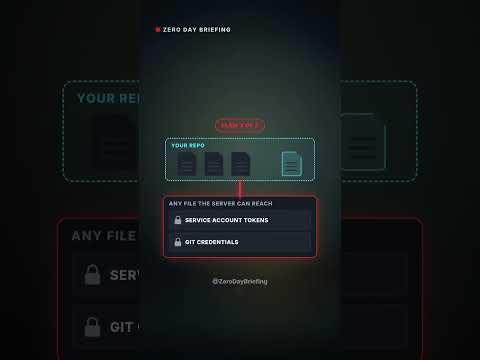
One poisoned commit could be enough to trigger three new 9.9 Critical flaws in Argo CD's repo server. Fixes are out: upgrade to 3.3.15, 3.4.10 or 3.5.4.
Three CVEs went public on October 20:
CVE-2026-113708, CVE-2026-113709 and CVE-2026-113672, each rated CVSS 3.1 9.9.
What they allow:
- Two can let a low privilege user run commands inside the repo server.
- The third can read any file the repo server can reach, including service account tokens and stored Git credentials.
The bar is low: pushing to a repository that Argo CD builds may be enough.
CISA's data records no exploitation so far, and the patched releases have been out since early October. Until you upgrade, lock down who can push to the repositories Argo CD builds and who has Application access.