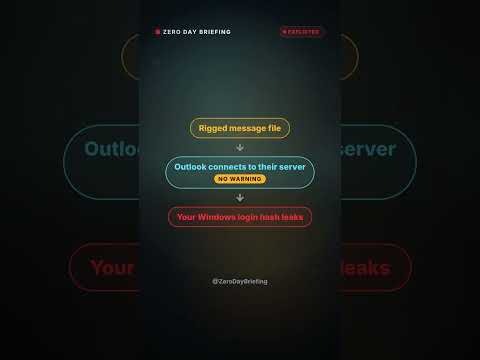
Microsoft just patched an Outlook zero day (CVE-2026-124194) that attackers are already exploiting in the wild.
What it does:
An attacker sends a rigged message file. If you open it, Outlook connects to the attacker's server without its usual warning and leaks your Windows login hash (NTLMv2). That can let attackers try to sign in as you.
The preview pane does not trigger it. You have to open the file.
Fixed in:
Microsoft 365 Apps (latest update)
Office LTSC 2021 (build 16.0.14334.21048)
Office LTSC 2024 (build 16.0.17932.21140)
How to update:
File → Office Account → Update Options → Update Now, or ask your IT team.
Context: this was the only exploited flaw among 1,095 Microsoft CVEs in the November 10, 2026 Patch Tuesday release. Microsoft rates it Moderate (CVSS 6.5).
Source: Microsoft Security Response Center (MSRC), CVE-2026-124194