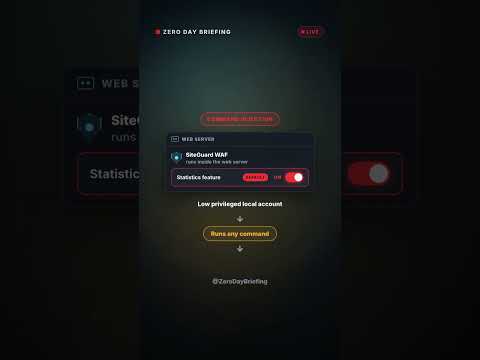
The firewall guarding your web server can hand local attackers root or SYSTEM, and it is being exploited right now.
SiteGuard Server Edition flaw: CVE-2026-106931
What you need to know:
• CISA added it to the Known Exploited Vulnerabilities list on Oct 20
• Federal patch deadline: Oct 23
• OS command injection in the statistics feature, which is on by default
• CVSS 7.8 (v3.0) / 8.5 (v4.0)
• Affected: Ver 2.20 and later
The fix:
• Ver 8.00 Update 5 (Apache/Nginx/IIS)
• Ver 7.00 Update 6 (FreeBSD)
• A file-replacement patch covers EOL builds
Before you patch: download the diagnostic info. Updating can erase evidence.
Sources:
CISA KEV: https://www.cisa.gov/known-exploited-vulnerabilities-catalog
JVN: https://jvn.jp/en/jp/JVN88474777/
Vendor alert: https://www.eg-secure.co.jp/siteguard/news/alert-202610-1