Your SonicWall VPN may let someone walk past MFA.
CVE-2026-19868: on firewalls with SAML single sign-on turned on for SSLVPN, someone with a valid password for another login method can bypass SAML, and the MFA prompt with it.
CISA lists it as actively exploited (added Nov 6, 2026). SonicWall advisory: SNWLID-2026-0014.
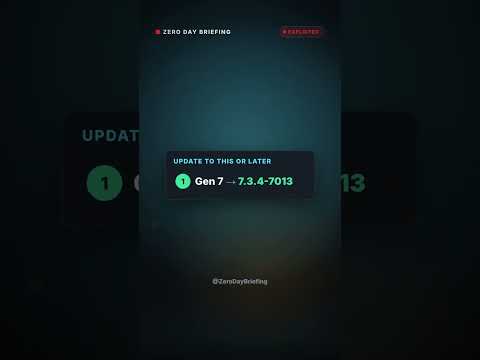
Fix: update Gen 7 to 7.3.4-7013 or later and Gen 8 to 8.2.3-8015 or later. Then review VPN logins that skipped your identity provider.