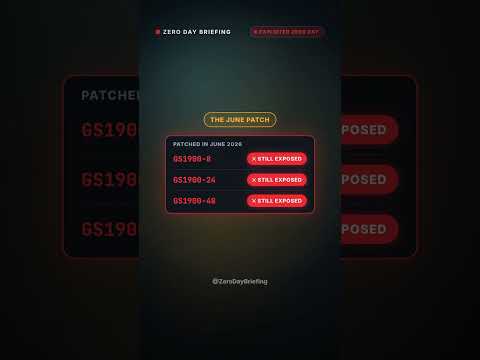
996 Zyxel GS1900 switches were hacked through a zero-day, and the June patch didn't cover this flaw.
What happened:
GreyNoise counted 996 compromised GS1900 switches in 48 countries. The attackers collected device configs and hashed root passwords.
The flaw:
CVE-2026-107441 (CVSS 8.8, High) is an unauthenticated bug in the web management interface. An attacker on an adjacent network can use it to run OS commands. Binarly found it still worked on firmware patched in June 2026 for an earlier bug (CVE-2026-7273).
What to do:
Install Zyxel's new firmware, released October 22, 2026, on every affected GS1900 model (24E, 8, 8HP, 10HP, 16, 24, 24EP, HPv2, 48, 48HPv2). As general hardening, keep the management page off untrusted networks.
Sources: BleepingComputer (Nov 4, 2026), GreyNoise, Binarly, Zyxel security advisory (Nov 3, 2026), CVE record CVE-2026-107441